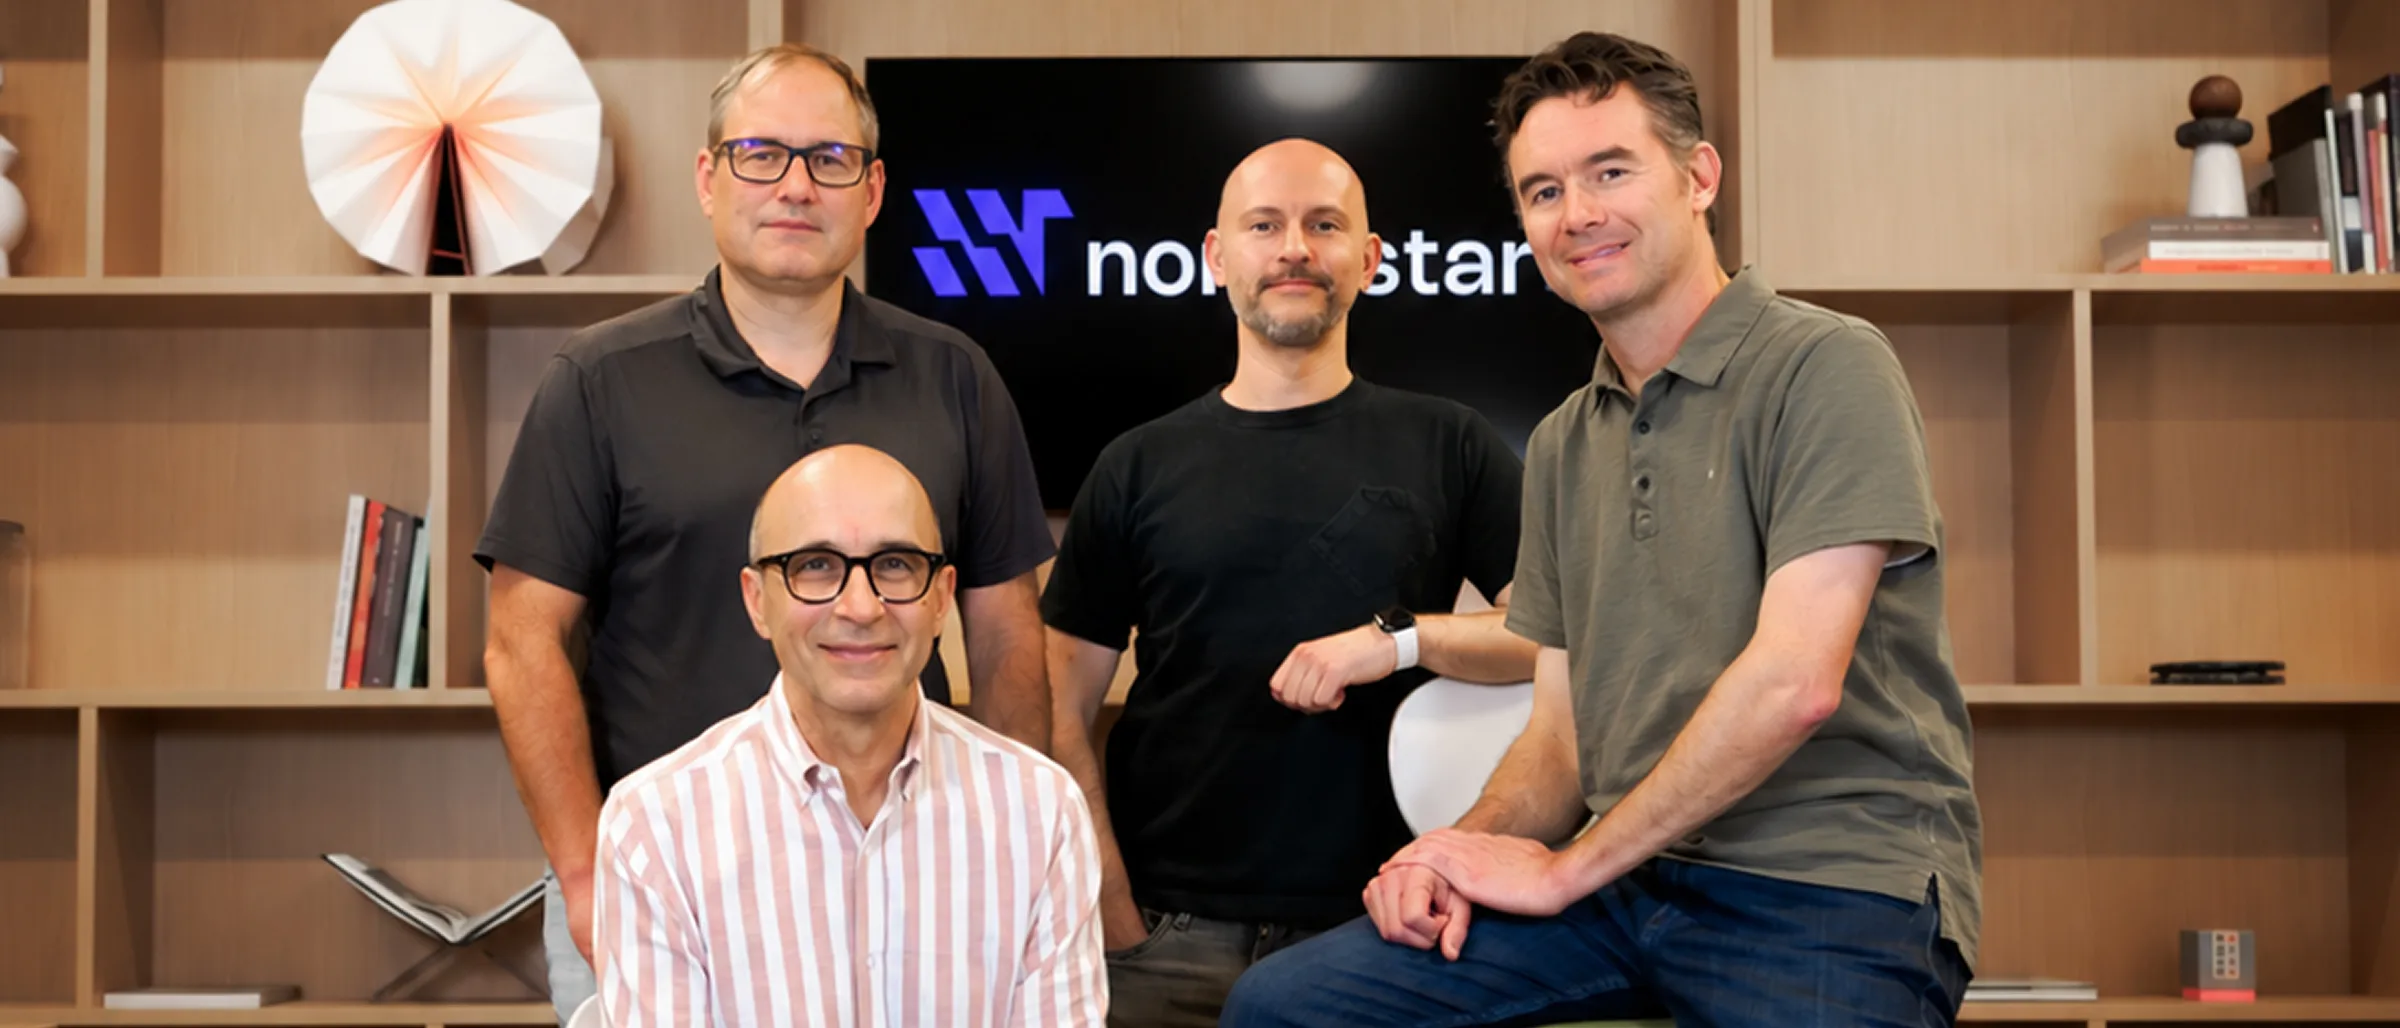
Why we founded Northstar
Software is shifting from SaaS to agents, and security will be one of the industries most transformed by it. But agents are only as good as their context. This is the story of why we started Northstar — and why context is the foundation of what comes next.
Software is undergoing one of its most fundamental shifts in decades.
For years, software was built around applications. We bought SaaS products, logged in, navigated dashboards, ran searches, created reports, and manually turned what we learned into action.
AI is changing that model.
We are moving from software as a service to software as an agent.
We believe security will be one of the fields most profoundly changed by this transition.
Instead of asking security teams to navigate dozens of applications and stitch together information themselves, AI agents will increasingly reason across data, make decisions, and act on their behalf.
But a fundamental problem stands in the way.
You can't build agents without context
Every system in a security organization knows something important, but none knows the whole story. Cloud security platforms understand infrastructure. Data security products understand sensitive data. Endpoint tools understand devices and agents. Vulnerability management systems understand vulnerabilities. Identity platforms understand users and permissions. Network security tools understand connectivity.
Traditional systems of record add another layer of knowledge: configuration management databases (CMDBs), ticketing systems, HR systems, asset databases, and other operational platforms.
To compensate for this fragmentation, security teams jump between consoles, export data to spreadsheets, write queries, correlate findings, open tickets, message other teams, and manually determine what actually matters.
An AI agent faces the same obstacle: it can reason effectively only when it understands the environment in which it operates.
Without context, there is no agentic security.
Building the context layer for agentic security
Northstar unifies security data across cloud security, data security, endpoint security, vulnerability management, identity and access, and network security with traditional systems of record, such as CMDBs and ticketing platforms.
We connect this information in a real-time context graph that understands not only individual assets, identities, vulnerabilities, configurations, and controls, but also the relationships among them.
That distinction matters.
Knowing that an endpoint has a vulnerability is data.
Knowing that the endpoint is internet-facing, contains sensitive data, is missing its EDR agent, has a critical vulnerability, and is accessible by an overprivileged identity is context.
And context changes what AI can do.
With the right context, agentic AI can accurately answer complex security questions, reason across an organization's environment, identify toxic combinations of risk, prioritize what matters, and determine what should happen next.
Context is also what will help security move from a reactive operating model to a proactive one. Whereas security has traditionally been about operating tools and manually coordinating workflows, agentic AI, guided by context, will shift security teams to defining policies, guardrails, and desired outcomes – and letting agentic AI continuously work toward them. This is a very different future for security.
Making security context available to any agent
We also believe this context should not be locked inside Northstar.
As organizations build their own AI agents with platforms such as Claude and other agentic frameworks, those agents need access to trusted, real-time security context.
That is where the Model Context Protocol (MCP) becomes important.
Northstar exposes its context graph through MCP, allowing authorized agents to access and reason over the connected security context Northstar has built.
Instead of integrating with dozens of security products, learning their individual data models, and recreating the relationships among them, an agent can access Northstar's context graph to get the security context it needs.
Imagine an agent built in Claude trying to determine whether a particular asset represents meaningful risk.
Instead of receiving isolated data points, the agent gets connected context it can reason over.
This makes Northstar more than an AI security application. Our context graph becomes a security intelligence layer that any authorized agent can use to understand the environment and take action.
As enterprises build more agents of their own, that shared intelligence layer becomes increasingly important.
In an agentic world, every agent needs context. Northstar provides the security context.
From answers to autonomous outcomes
But better answers are only the beginning.
The real opportunity for AI in security is not another chatbot layered on top of security data.
It is turning intelligence into action.
Once Northstar understands the relationships across the security environment, teams can build workflows that continuously identify risk and autonomously drive security outcomes.
Consider endpoint security.
Instead of a security analyst periodically running a report to find machines with unhealthy or missing EDR agents, Northstar can continuously identify which endpoints should be protected, detect gaps or unhealthy coverage, incorporate each asset’s business and security context, and initiate the appropriate remediation workflow.
The same model applies to identity and access.
Northstar can continuously identify excessive privileges or inappropriate access, understand the surrounding user, application, asset, and risk context, and drive the workflow needed to remediate it.
These workflows can be created in Northstar and run continuously and autonomously. They can generate dashboards and reports, send notifications, create and route tickets, trigger remediation, and validate that an issue has been resolved.
The result is a fundamental shift: security teams move from finding problems and coordinating remediation to defining the outcomes they want and allowing AI agents to work continuously toward them.
Security should become proactive
Security has historically been reactive.
Find the vulnerability. Investigate the alert. Review the access. Open the ticket. Chase the owner. Fix the problem. Run another report to confirm the fix.
Agentic AI gives us an opportunity to change that operating model fundamentally.
Imagine a security platform that continuously understands your environment, reasons about changes as they happen, identifies combinations of risk before they become incidents, and autonomously takes the appropriate action.
The security team moves from operating tools and manually coordinating workflows to defining policies, guardrails, and desired outcomes.
That is a very different future for security.
And we believe context is the foundation for that future.
Why now
The transition from SaaS to agents is already underway.
As AI becomes more capable of reasoning and acting, the value of software will increasingly move beyond the interface to the intelligence, context, and workflows underpinning it.
Security has an enormous opportunity in this transition because the industry already has tremendous amounts of data. What has been missing historically is a way to connect that data, understand the relationships within it, and make the resulting context available to AI.
We started Northstar to build the real-time context layer for agentic security.
Northstar gives AI the understanding it needs to reason across the security environment, makes that context available to other agents through MCP, and enables security teams to turn intelligence into autonomous outcomes.
Because in an agentic world, the advantage will not belong to the platform with the most data. It will belong to the platform that can turn data into context – and context into action.
That is the future we are building at Northstar.
October 27, 2026
Northstar Security emerges from stealth with $7M to uncover hidden cyber risks and put AI agents to work
Backed by Wing Venture Capital, Northstar exposes toxic combinations lurking across disconnected security systems and gives AI agents the context to act
Backed by Wing Venture Capital, Northstar exposes toxic combinations lurking across disconnected security systems and gives AI agents the context to act
SAN FRANCISCO – Oct. 28, 2026 – Northstar Security today emerged from stealth with $7 million in seed funding led by Wing Venture Capital to address one of cybersecurity’s biggest challenges: security teams have more data and tools than ever, but still lack the connected context needed to understand risk and take action. Northstar’s agentic AI platform connects security and IT data through a real-time Security Context Graph, uncovering hidden risks and toxic combinations while enabling AI agents to investigate and help resolve them. The funding will accelerate product development, team expansion and go-to-market efforts.
Security has a context problem
Enterprises have spent billions on tools to detect threats, vulnerabilities and misconfigurations, yet critical security information remains fragmented across disconnected systems. A vulnerability, unmanaged device or overprivileged identity may appear manageable in isolation. When combined, they can create dangerous exposures that put critical business systems at risk.
Uncovering these toxic combinations requires analysts to piece together information across multiple tools, investigate relationships, assess business impact and coordinate fixes. The process can take hours, leaving security teams buried in manual work.
Northstar changes that equation by creating the context foundation that makes agentic security possible. Its real-time Security Context Graph maps relationships among assets, identities, vulnerabilities, applications and business systems to give both humans and AI agents a shared understanding of the environment. With that foundation, Northstar can answer complex security questions, identify previously hidden exposures, and orchestrate autonomous remediation workflows, with human oversight where appropriate.
“Security teams are drowning in data but starving for context,” said Amer Deeba, CEO and co-founder of Northstar Security. “We’ve spent decades building better tools to find security problems, but connecting the dots and fixing them remains painfully manual. We believe the next generation of security won’t be defined by more dashboards or alerts. It will be powered by AI agents that understand the full context of an organization’s environment and can take proactive action. That’s why we built Northstar: to provide the context foundation for agentic security and move the industry from finding problems to continuously fixing them.”
Led by Wing Venture Capital, the round also included participation from MVP, Outliers and cybersecurity industry veterans Gerhard Eschelbeck, Renaud Deraison and Justin Somaini.
“The cybersecurity industry has spent billions building better ways to find problems, yet security teams are still struggling to keep up with the risks they’ve uncovered,” said Jake Flomenberg, Partner at Wing Venture Capital. “Northstar is challenging decades of conventional thinking by giving AI agents the context to understand what’s happening and the ability to do something about it. We believe it has the potential to fundamentally rewrite the security playbook.”
From disconnected signals to autonomous action
Consider a common security problem: a company laptop without endpoint protection. Identifying the device may require navigating six different tools to determine who owns it, what systems it can access and whether it poses a meaningful risk. Hours later, the analyst may have the answers, but the device remains unprotected.
With Northstar, an analyst can ask those questions in natural language and quickly see the relationships that matter. The platform can reveal, for example, that an unprotected laptop belongs to a privileged user with access to a business-critical payroll system. Northstar’s AI agents can then initiate remediation workflows to deploy endpoint protection, notify the owner or restrict risky access, with human oversight where appropriate.
Northstar also makes its Security Context Graph available to external AI agents through Model Context Protocol (MCP), enabling organizations to build their own security workflows using Claude and other AI tools. The result is a fundamental shift from investigating isolated security findings to understanding interconnected risks and taking action to resolve them.
“Security teams don't need another dashboard generating more findings. We need to connect the data we already have, understand what matters, and turn that context into action,” said Randy Barr, CISO, Cequence Security. “Northstar lets us do exactly that, using agentic workflows to continuously identify and remediate security issues. This is where security is heading: from finding problems to continuously fixing them.”
Northstar’s platform brings together three capabilities:
- Connected Security Context: A real-time Security Context Graph that unifies assets, identities, vulnerabilities, configurations, and business relationships across existing enterprise systems.
- Context-Driven Risk Intelligence: AI-powered analysis that answers complex questions, exposes hidden risks and toxic combinations, and prioritizes issues based on their potential business impact.
- Agentic Remediation: Intelligent agents and workflows that turn findings into actionable outcomes, coordinating fixes across systems and teams with appropriate human oversight.
Today, Northstar supports more than 70 integrations across enterprise security and IT systems, including AWS, Google Cloud, Microsoft Defender, Microsoft Entra, Okta, GitHub, Slack, Workday, and Zendesk.
“The next generation of security operations won’t be measured by how many alerts teams can process, but by how quickly they can proactively resolve risks,” said Gerhard Eschelbeck, former CISO of Google and an investor in Northstar Security. “Northstar is enabling that shift by giving AI agents the context to move from investigation to autonomous action.”
Northstar was founded by Amer Deeba and Ed Rowe, who first worked together at Adobe in the late 1990s. Deeba previously co-founded Normalyze, acquired by Proofpoint, and held senior leadership roles at Qualys. Rowe, Northstar's CTO and co-founder, previously served as CTO of Farmers Business Network and Senior Vice President of Engineering at AppDynamics. The founding team combines decades of experience building enterprise software, security platforms, and large-scale data infrastructure.
Northstar is available today and organizations can request a demonstration at northstar.security/request-a-demo.
About Northstar Security
Northstar Security is building the context foundation for agentic security. Its AI-powered platform transforms fragmented security and IT data into a real-time Security Context Graph, enabling organizations to understand their security environment, uncover hidden risks and toxic combinations, and orchestrate autonomous remediation workflows. By connecting security intelligence directly to action, Northstar helps enterprises move beyond finding problems to continuously fixing them. For more information, visit northstar.security.
No resources match your search.
The Expert Security Assistant for the Agentic AI Era
Stop searching across dozens of tools. Start asking smarter questions – and building autonomous security outcomes.